

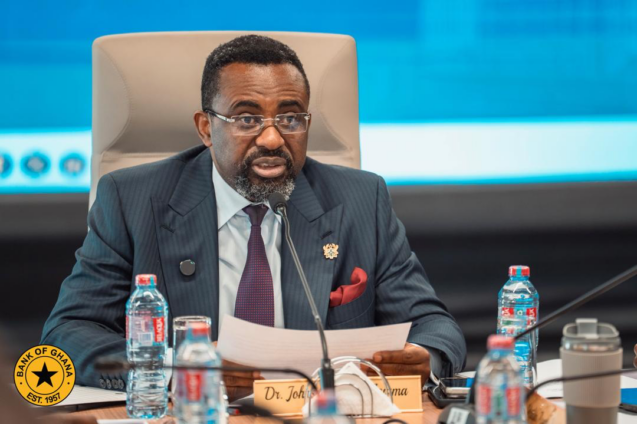
The Bank of Ghana (BoG) has directed banks to strengthen the independence and effectiveness of their fraud management functions, including giving fraud units direct and unrestricted access to managing directors and chief executive officers.
Governor Dr. Johnson Asiama issued the directive at a meeting with the heads of banks at the Bank Square in Accra on October 6, 2026, following concerns raised by the Ghana Association of Banks (GAB) about the inconsistent ways banks currently position their fraud functions. The directive places fraud management closer to the centre of corporate decision-making at a time when banks are grappling with increasingly sophisticated financial crime, cyber threats and technology-related risks.
The Directive: Independence and Unrestricted Access
At the heart of the directive is the demand for stronger independence for fraud management teams. Dr. Asiama said banks must ensure that their fraud functions are positioned in a manner that allows them to escalate serious concerns without unnecessary internal barriers.
“The fraud function should be appropriately positioned with direct and unrestricted access to the managing director or chief executive officer,” Dr. Asiama said.
The requirement could significantly change how some banks structure their internal fraud controls. Rather than having fraud-related concerns filtered through several layers of management, the new arrangement is designed to give responsible officers the ability to raise critical issues directly with senior executives. That access could prove important when suspected fraudulent activity involves senior personnel, major transactions or weaknesses that require immediate intervention.
Higher Standards for Fraud Professionals
The central bank is also looking beyond organisational structures. Dr. Asiama directed banks to ensure that personnel responsible for fraud management possess the requisite skills, professional certifications and technical competence.
The emphasis reflects the changing nature of financial fraud. Criminal activity affecting banks is no longer limited to traditional schemes involving forged documents or unauthorised transactions. Digital banking, mobile applications, electronic payments and interconnected financial platforms have created new opportunities for criminals to exploit weaknesses in systems and processes. Fraud teams therefore need technical knowledge that matches the sophistication of the risks confronting financial institutions. Banks will increasingly need personnel who can identify unusual transactions, investigate suspicious activity, understand digital vulnerabilities and respond quickly when fraud incidents emerge.
Ghana’s Escalating Fraud Landscape
The directive comes amid a marked escalation in fraud incidents across Ghana’s banking sector. According to the Ghana Association of Banks’ Industry Fraud Report for January to March 2026, member banks reported 73 confirmed fraud cases with a total attempted exposure of approximately GH¢14.05 million. Of this amount, GH¢12.05 million emerged from successful cases, with recoveries of about GH¢1.01 million, resulting in a net loss of GH¢11.05 million.
The report identified Cash Suppression/Theft as the largest contributor to losses, with nine cases resulting in a net loss of GH¢5,002,427.23. Card/POS fraud followed with 18 cases and a net loss of GH¢3,244,083.23, while Forgery (including document alteration) accounted for four cases with a net loss of GH¢1,923,201.54. E-Transfer fraud recorded GH¢261,401.50 in losses across just two cases.
A key structural concern highlighted in the report is the consistently low recovery rate, particularly in digitally executed frauds where funds are rapidly dispersed across multiple wallets and platforms, making recovery difficult. The report noted that fraud is now primarily human-driven rather than system-driven, with fraudsters manipulating customers, staff, or trusted relationships rather than hacking banking systems. Internally driven fraud cases, while fewer in number, were found to be more recoverable, likely due to traceability and institutional control over staff.
At the industry level, the CEO of the Ghana Association of Banks, John Awuah, has warned that fraud incidents pose the biggest threat to Ghana’s digital trust. Speaking in July 2026, he revealed that Ghana’s digital payments ecosystem processes about 10 billion transactions valued at approximately GH¢4.5 trillion annually, with around 20,000 fraud cases recorded and estimated losses of about GH¢100 million. “We are not there yet. But are we heading there? I would say yes,” he said, referring to a potential digital trust crisis.
The Cyber Security Authority recorded 3,876 cybersecurity incidents between January and July 2026, with online fraud making up roughly 47 percent of them. Fraud cases reported by banks and payment service providers increased by about 48 percent in 2025, with funds worth more than GH¢100 million placed at risk.
The Cyber and Information Security Directive (CISD) 2026
The fraud governance directive is part of a broader regulatory overhaul under the Bank of Ghana’s revised Cyber and Information Security Directive (CISD) 2026, launched in Accra on March 26, 2026, under the theme “A Safer and More Resilient Digital Financial Industry.”
The CISD 2026 redefines governance, cloud hosting, AI/ML use, mobile channel protection and incident reporting across the financial sector, tiered by institution size. Key pillars include strong governance structures, artificial intelligence and machine learning governance, cloud computing security, and a proportionality framework emphasising board-level oversight and expertise in cyber risk management.
Governor Asiama said the new directive was designed to move Ghana’s financial sector from compliance to active cyber resilience, embedding security into governance, operations and institutional culture. Unlike the previous 2018 directive that focused on universal banks, the new one expands the Financial Industry Command Security Operations Centre’s (FICSOC) work to actively onboard all savings and loans companies, microfinance institutions, fintechs and partner regulators.
On governance and accountability, the directive requires that at least one board member of every regulated institution possess verifiable expertise in cyber risk management. On cloud computing, the directive does not endorse the wholesale migration of core systems or sensitive data to the cloud, invoking the Cybersecurity Act 2020 and the Data Protection Act 2012 to ensure that only non-sensitive front-end services may be hosted in the cloud. The proportionality framework ensures that a small rural bank is not held to the same standard as a large multinational.
The Chief of Staff, Julius Debrah, who launched the directive, emphasised that cybersecurity must be treated as a pillar of economic stability, urging Ghana’s financial sector to embed cyber resilience at the core of its operations to safeguard public trust and national development.
Fraud Intelligence Hub in Development
The BoG is also developing a fraud intelligence hub to enable financial institutions to share information on emerging fraud patterns and threats. Daniel Kulu, Director of Information Security at the BoG, said the central bank is moving towards a more collaborative and intelligence-led approach to combating financial fraud. “Digital finance is expanding faster than the guardrails around it, and closing that gap is a shared responsibility,” he said, noting that the BoG has revised its Cyber and Information Security Directive to address emerging threats including risks linked to artificial intelligence, cloud computing and data security.
Bank of Ghana’s Broader Supervisory Push
The fraud governance directive is the latest in a series of supervisory interventions by the BoG under Governor Asiama’s leadership. In June 2026, the central bank warned banks over the rising use of forged land documents to secure loans, with Dr. Asiama expressing concern over increasing cases of fraudulent land title documentation and forged ownership records used to secure credit facilities. He called for clear rules on handling third-party collateral and firm action against staff involved in fraudulent activities.
In May 2026, at the 3i Africa Summit in Accra, Dr. Asiama warned that weak authentication systems in Ghana’s expanding digital financial sector were threatening public trust and increasing the risk of fraud. “Confidence will depend on the strength of our digital identity and KYC frameworks. Weak authentication increases fraud risk, affects credit quality, and undermines trust in digital financial services,” he said.
What the Directive Means for Banks and Consumers
For banks, the directive signals that having a fraud department alone will not be enough. Institutions must ensure that the function is properly empowered and staffed with competent professionals who can operate independently of other business lines. The requirement for direct CEO access could mean restructuring reporting lines, particularly at banks where fraud units currently report through risk, compliance or operations departments.
For consumers, the directive is expected to strengthen protection against fraud, particularly as digital banking, mobile money and electronic payments continue to grow. Bank customers have increasingly expressed reluctance to carry out even routine transactions due to fears of being defrauded. The GAB CEO has noted that although the financial impact of fraud is significant, the banking sector is more concerned about the increasing number of fraud cases because they shape public perception and confidence in digital platforms.
The BoG’s directive forms part of a broader effort to build a safer and more resilient digital financial industry in Ghana, where mobile money flows reached more than GH¢40 billion in June 2026, with transactions processed through mobile money platforms close to GH¢493 billion. As the BoG continues to intensify its supervisory focus on cyber technology, customer-fund safeguarding and third-party risks, banks will be expected to demonstrate tangible improvements in their fraud governance frameworks in the months ahead.